What Your Cookie Banner Actually Needs to Be GDPR Compliant
Cookie consent banners have become universal across the modern web, yet industry audits consistently find that the majority of live implementations fail to meet basic European data protection standards. A pre-checked checkbox, a banner that disappears on scroll, or a popup with no visible “Reject” option is not merely an imperfect user interface—it is non-compliant under the law.
For software engineers, product managers, and founders, implementing a compliant consent management system is not about slapping a generic modal over a web page. It is about understanding the boundary between the General Data Protection Regulation (GDPR), the ePrivacy Directive, and the browser runtime where scripts actually execute.
This guide walks through the exact legal requirements, the most common implementation pitfalls, and practical engineering steps to build a cookie consent architecture that respects user privacy while maintaining critical website functionality.
The Legal Foundation: GDPR vs. ePrivacy Directive
A frequent point of confusion among web developers is which law actually governs cookies. The rules stem from two distinct European legal frameworks:
- The ePrivacy Directive (Directive 2002/58/EC, Article 5(3)):Often called the “Cookie Law,” this regulation establishes that storing or accessing information on a user’s terminal equipment (including cookies, local storage, indexedDB, and device fingerprinting) requires prior informed consent, unless the storage is strictly necessary for providing an explicitly requested service.
- The GDPR (Regulation (EU) 2016/679, Article 4(11) & Article 7): While the ePrivacy Directive defines when consent is needed, the GDPR defines what valid consent actually means. Under GDPR, consent must be freely given, specific, informed, and unambiguous, demonstrated through a clear affirmative action.
Together, these two laws mean you cannot place advertising pixels, analytics trackers, or cross-site identifiers onto a visitor’s device until that visitor has made an active, informed choice to allow it.
The 6 Most Common Cookie Banner Failures
European regulatory bodies—such as France’s CNIL, Ireland’s DPC, and Germany’s supervisory authorities—have issued millions of euros in penalties for deceptive consent interfaces. If your website exhibits any of the following patterns, your banner fails compliance:
1. Missing or Buried “Reject All” Button
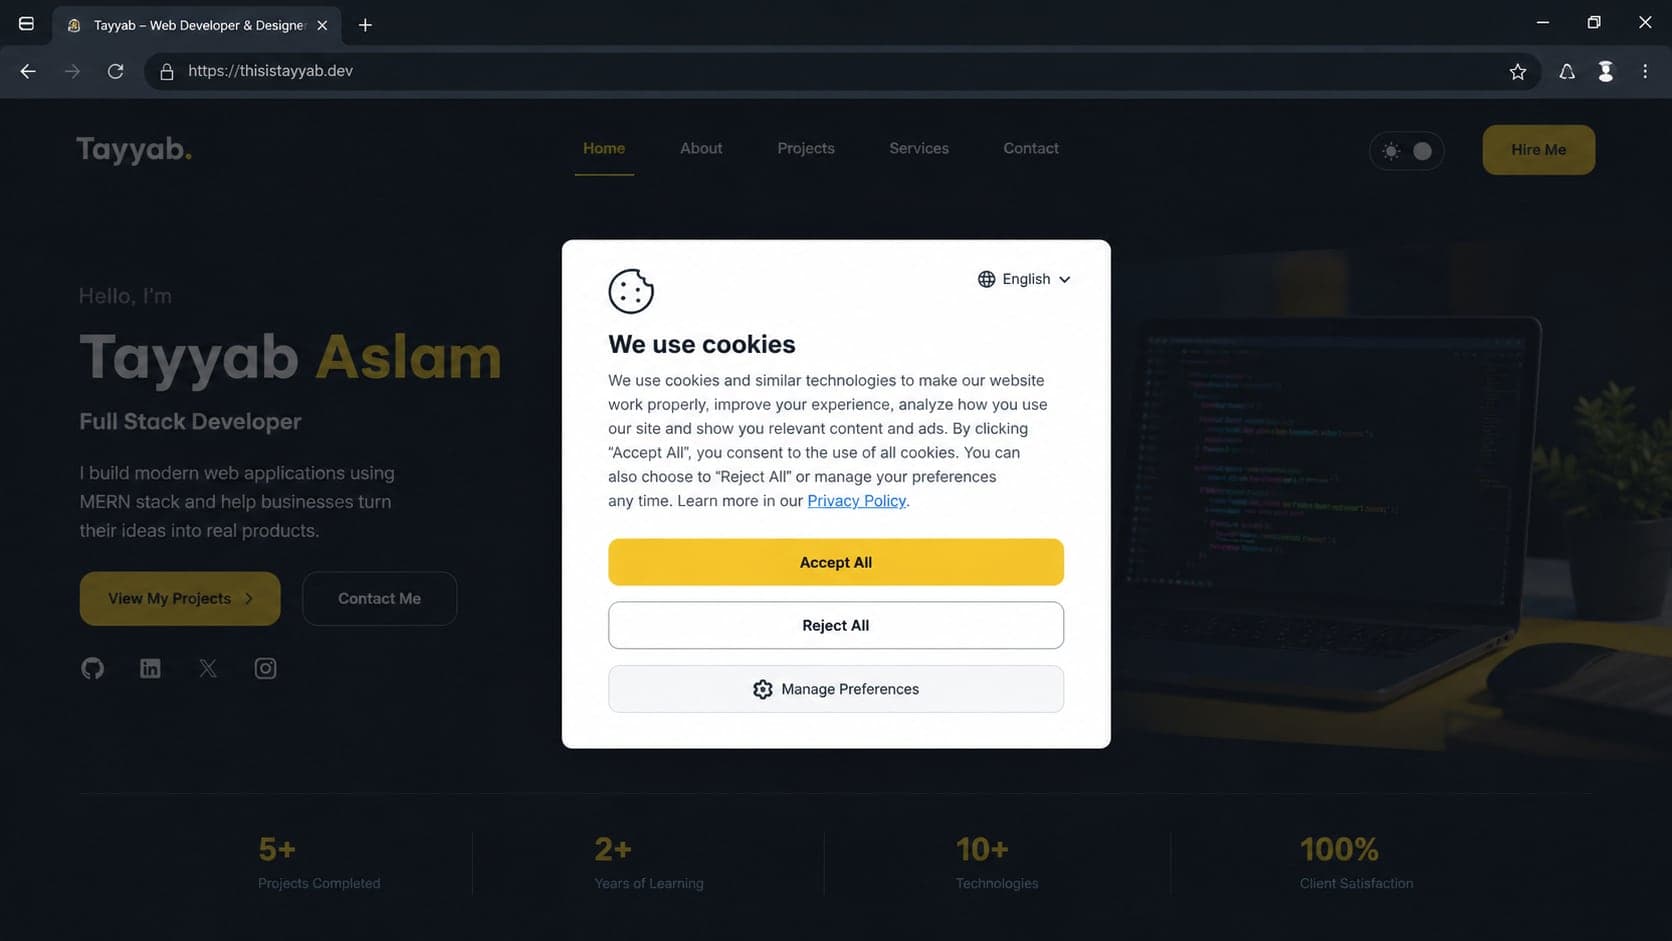
Providing a large, contrasting “Accept All” button alongside a subtle “Manage Preferences” link that forces users through multiple sub-menus to decline cookies is unlawful. Regulators require that rejecting cookies must be as direct, immediate, and visually balanced as accepting them. Both options must exist at the exact same level of the interface.
2. Firing Non-Essential Scripts Before Consent (“Ghost Firing”)
The most common technical error is rendering third-party scripts in the document <head> before the visitor clicks anything. If your page loads Google Tag Manager, Meta Pixel, or Hotjar on initial page render while displaying a banner that says “By continuing to browse, you accept cookies,” you have violated prior consent. Non-essential scripts must remain completely blocked until affirmative consent is registered.
3. Pre-Ticked Preference Checkboxes
In the landmark Planet49 ruling (Case C-673/17), the Court of Justice of the European Union (CJEU) confirmed that pre-ticked checkboxes do not constitute valid consent. In a preferences modal, all non-essential categories (Analytics, Marketing, Personalization) must default to unchecked / off.
4. Implied Consent via Scrolling or Continued Browsing
Banners stating “By scrolling this page or clicking any link, you agree to our use of cookies” have been explicitly prohibited by the European Data Protection Board (EDPB Guidelines 05/2020). Scrolling is not an unambiguous affirmative action. Inactivity or continued navigation cannot be interpreted as positive consent.
5. The Cookie Wall
Blocking access to public website content behind an impenetrable overlay that forces users to accept tracking cookies violates the requirement that consent be “freely given.” While paywalls that offer a paid alternative to tracking are subject to nuanced regional debate, denying access strictly to enforce ad tracking is non-compliant.
6. No Visible Method to Withdraw Consent Later
GDPR Article 7(3) dictates that it must be as easy to withdraw consent as it was to give it. Once a user accepts or rejects cookies, they must have a persistent way to change their mind—such as a small floating “Cookie Preferences” badge in the corner of the screen or a direct link in the site footer.
The 4 Cookie Categories Explained
To architect a compliant consent mechanism, every cookie, local storage key, and tracking script on your website must be classified into one of four standard categories:
| Category | Purpose & Scope | Prior Consent Required? | Typical Examples |
|---|---|---|---|
| Strictly Necessary | Core technical functions requested by user (auth, cart, security, consent record). | NO (Exempt) | session_id, csrf_token, cookie_consent |
| Functional / Preferences | Remembers user settings like language, currency, or theme choices across visits. | YES (Conditional) | ui_theme, user_locale, font_size |
| Analytics / Performance | Measures page visits, traffic sources, scroll depth, and bounce rates. | YES (Mandatory) | _ga, _gid, _pk_id, amp_* |
| Marketing & Retargeting | Tracks users across websites to build behavioral profiles and display personalized ads. | YES (Mandatory) | _fbp, IDE, personalization_id |
The 5-Step Engineering Implementation Guide
Building a compliant consent system in modern frontend frameworks (such as Next.js, React, or standard vanilla JavaScript) requires a structured execution plan:
Step 1: Audit All Client-Side Scripts
Open Chrome DevTools, navigate to the Application > Cookies tab, and refresh your website in an Incognito window. Any cookie that appears before you click an accept button represents a potential compliance defect. Document every vendor script running on your domain.
Step 2: Implement Conditional Script Loading
Never include raw analytics or marketing script tags directly in your HTML template. Instead, manage them through a centralized consent dispatcher. In modern web applications, this can be achieved using dynamic script injection or Google Consent Mode v2:
// Initialize Google Consent Mode v2 with default denied states
window.dataLayer = window.dataLayer || [];
function gtag(){dataLayer.push(arguments);}

gtag('consent', 'default', {
  'ad_storage': 'denied',
  'ad_user_data': 'denied',
  'ad_personalization': 'denied',
  'analytics_storage': 'denied',
  'wait_for_update': 500
});

// Update consent dynamically when the user clicks "Accept All"
function onConsentGranted() {
  gtag('consent', 'update', {
    'analytics_storage': 'granted',
    'ad_storage': 'granted',
    'ad_user_data': 'granted',
    'ad_personalization': 'granted'
  });
}
Step 3: Build the First-Layer Consent Interface
Ensure your banner modal contains three distinct elements on the primary view:
- A concise statement explaining why cookies are used and linking to your Cookie Policy.
- An “Accept All” button.
- A “Reject Non-Essential” button styled with identical visual prominence (avoid hiding it in low-contrast text).
- A “Customize” button that opens detailed category toggles.
Step 4: Persist Consent State
Store the user’s decision in a first-party cookie or local storage key (e.g., taylance_cookie_consent) containing a timestamp, the version of your cookie policy, and the boolean state of each category. Set an expiration window between 180 and 365 days.
Step 5: Provide a Permanent Withdrawal Mechanism
Place a “Cookie Settings” link in your website footer alongside your Privacy Policy and Terms & Conditions. Clicking this link must re-open the preferences modal, allowing the visitor to revoke consent at any time with a single click.
Compliance as Trust Infrastructure
Many business owners worry that providing an easy “Reject All” button will destroy their website analytics. While opt-in rates may adjust, privacy-first architecture creates significant long-term advantages:
- Protection from Regulatory Fines: EU data protection authorities regularly issue automated fines to websites ignoring basic consent mechanics.
- Faster Page Speed: Blocking non-essential tracking scripts until consent is granted drastically improves Core Web Vitals, initial server response times, and mobile responsiveness.
- Corporate Procurement Readiness: Enterprise clients and institutional partners conduct privacy audits before signing vendor contracts. A clean, compliant frontend proves professional engineering discipline.
For teams building custom digital experiences, compliance should never be an afterthought. At Taylance Tech, we build compliant, high-performance web applications engineered to meet international data standards from day one. Explore our custom web development services or contact our engineering team to audit your current frontend architecture.
FAQ
Frequently Asked Questions
Quick answers to common questions about this topic.
Is a 'Reject All' button legally required on the first layer of a cookie banner?
Yes. Data protection authorities across the European Union (including France's CNIL, Ireland's DPC, and Germany's DSK) have made it clear that refusing consent must be as easy as giving it. If your banner features a prominent 'Accept All' button, it must provide an equally accessible and visually balanced 'Reject All' button on the same initial screen.
Do I need consent for Google Analytics under GDPR?
Yes, in standard configurations. Standard analytics cookies that track user identifiers, client IDs, or cross-device journeys require prior consent under the ePrivacy Directive. If you use Google Analytics 4, consent must be granted before the gtag measurement script initializes, or you must configure Google Consent Mode v2 to deny analytics storage by default.
Can I block users from my website if they refuse cookies (cookie wall)?
Under GDPR guidelines established by the European Data Protection Board (EDPB), cookie walls are generally non-compliant because consent must be 'freely given'. Forcing a user to accept non-essential tracking cookies as a condition of accessing public content invalidates that consent.
Are strictly necessary cookies exempt from consent banners?
Yes. Cookies that are strictly necessary to deliver a service explicitly requested by the user—such as authentication session tokens, shopping cart state, CSRF security tokens, and the cookie that stores the user's consent choice itself—do not require prior consent.